Information Security
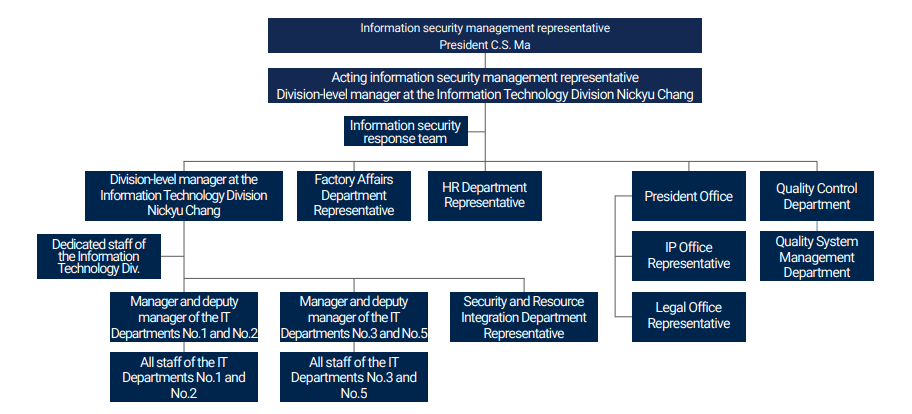
The Group established the Information Security Committee with 5 information security personnel, held quarterly information security meetings, and held an information security management review meeting every year. The President serves as the representative of information security management, regularly reporting the Company’s information security system performance to the highest level of management and reviewing the Company’s information security policies and goals. An Information Security Response Team has been established under the Information Security Committee. The team members are drawn from various departments and are required to receive regular information security response training. The team is responsible for planning information security incident response procedures and convening relevant personnel to conduct drills and exercises.
The Group issued its “Information Security Policy”, which specifies rules for employees to abide by, strictly implementing information security policies and measures to protect customer privacy to ensure that the Company’s trade secrets and customer information are not leaked. The Company has also consistently received ISO 27001 certification to ensure the confidentiality, integrity, and availability of information assets. There were no major cybersecurity incidents in our company in 2025, nor did any lead to the loss of customer or related information.
Information Security Policies and Emergency Response Mechanisms
To maintain the confidentiality, integrity, and applicability of Phison’s assets and protect users’ information privacy, we clearly stipulated in our information security policies that employees shall avoid unauthorized access and revisions while respecting intellectual property rights and protecting the information of customers and the Company. Anyone who discovers information security incidents or suspicious security weaknesses should report them to the Information Department through our reporting mechanism, at which point our Information Department personnel will conduct proper investigations and handle the matter appropriately.
It is the responsibility of all Phison personnel to follow our Information Security Policies. Company personnel who violate our information security policies shall face civil, criminal, or administrative responsibilities according to the severity of the violation, or penalties according to relevant rules. The policies are also integrated with the Company’s employee performance evaluation to reduce instances of employees being penalized or facing legal responsibilities due to information security violations and also reduce the Company’s information security risks.
Reporting Procedures for Suspicious Information Security Risks

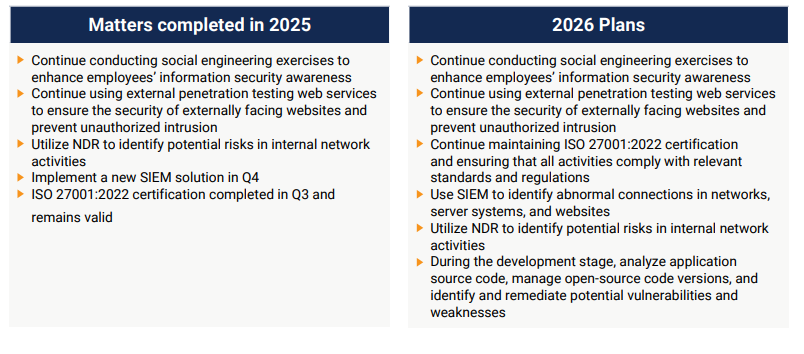
In accordance with ISO 27001 certification guidelines, the Company conducts an annual internal audit, followed by an external audit conducted by a third-party certification. No major deficiencies have been found in recent years. The Company regularly conducts recovery drills on important core systems every year to test the effectiveness of their recovery procedures, ensuring that the Company’s system can continue to operate even if subject to natural disasters or malicious attacks. The Company also performs regular vulnerability scanning and has in place a third-party security risk analysis platform to detect vulnerabilities in external service sites, continuing to improve and strengthen information security protection. The ratings are all maintained at level A (90 points and above). Besides, the Company joined the Taiwan Computer Emergency Response Team/Coordination Center(TWCERT/CC) information security alliance, enhanced information security protection by using the information security information sent from the TWCERT/CC, examined each piece of internal equipment, updated systems, and fixed vulnerabilities.
Information Security Education Training
The Group’s information security education and training is coordinated by the Enterprise System Integration Division. Information security announcements and promotions are conducted on a quarterly basis to enhance employees’ information security awareness. In 2025, the cybersecurity announcement topics issued by the Enterprise System Integration Division included awareness of business email compromise and spam emails, legitimate software licensing and weak password change guidance, social engineering exercises, detection of suspicious phone impersonation attempts to obtain employee information, and prevention of phishing attacks through contact forms. In 2025, the information security training program included an introduction to information security, information security incident reporting channels, cybersecurity threats and preventive measures, employee information security guidelines, and awareness training on social engineering attack prevention (with total employee training hours reaching 5,081.5 hours). All employees completed the information security training at a 100% completion rate.
Information Security Risk Management Plan